Verify endpoint access
Confirm approved IP addresses, interfaces and independent MMS associations for the installed devices.
Use ARSAS to reconfirm live IED communication after installation, verify selected values and reports, inspect GOOSE traffic, test approved control paths and isolate site-specific integration problems.
Installation, network addressing, gateway mappings, switch configuration and final project files can introduce differences that were not present during FAT.
Confirm approved IP addresses, interfaces and independent MMS associations for the installed devices.
Use available SCL as project intent while checking the data model and services actually exposed by the IED.
Confirm required DataSet coverage, RCB state, quality, timestamps and reason-for-inclusion evidence.
Check APPID, VLAN, destination MAC, sequence counters, retransmission and ordered payload against the site design.
Use per-IED diagnostics to distinguish association, report, frame, gateway, file-service and command-completion problems.
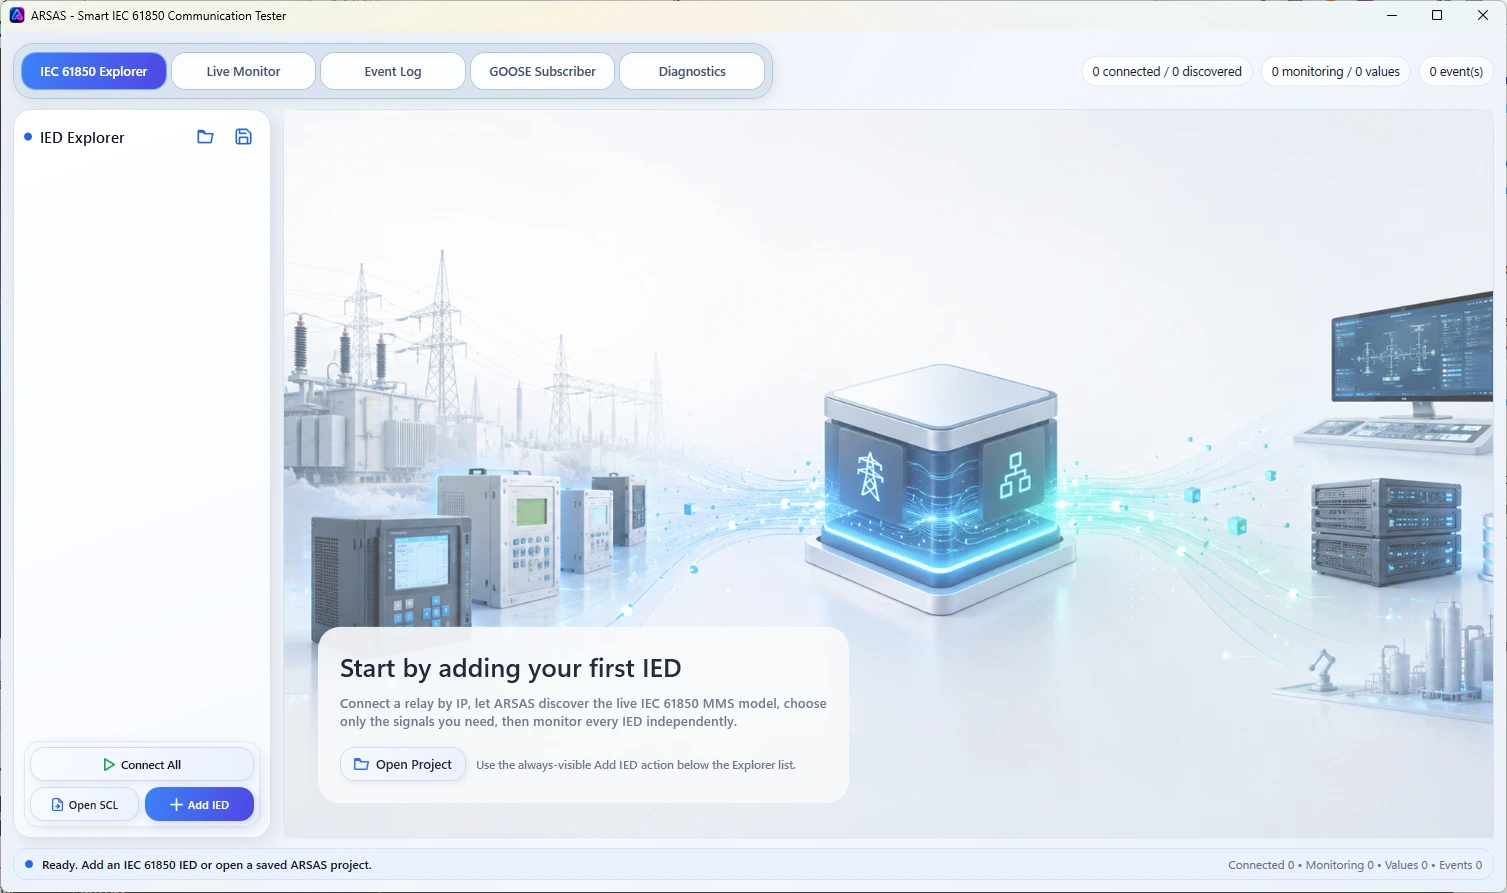
Keep model, monitoring, reporting, events, files and diagnostics attributable to each IED while validating the integrated substation system.
ARSAS does not replace approved site procedures, network-security authorization, injection testing, wiring checks, protection-setting verification, switching control or customer acceptance records.
Installer and portable packages share the same application scope. Verify the published SHA-256 and review the release boundary before field use.
Release notes, limitations and signing status →